How to Remove EXIF Data From Photos Without Uploading
Table of Contents
What EXIF data actually contains
EXIF is a block of key-value fields the camera writes at the moment of capture. A phone photo with location services enabled can easily contain 40 or more distinct fields. The ones worth knowing about:
Location. GPS latitude, longitude, and sometimes altitude — accurate to a few meters. Not your neighborhood: your exact spot. Some photos even record which direction the camera was pointing.
Timestamps. The exact date and time of the shot, often to the second — some files carry a separate GPS timestamp that can differ from the local clock.
Device details. Camera make and model ("Apple iPhone 16 Pro"), the camera's serial number — which identifies your specific device — lens info, and the software that processed the image.
Capture settings. Shutter speed, aperture, ISO, focal length, flash, white balance. Harmless alone, but together they fingerprint your gear.
Content extras. An embedded thumbnail that can be an uncropped version of the photo if you cropped after shooting, plus an artist field some cameras fill with the owner's name.
None of this is visible in the picture itself. It rides along silently in the file — which is exactly why it is so easy to forget.
Why it is a privacy problem, not a trivia fact
The most famous EXIF story is also the bluntest. In December 2012, a Vice journalist interviewing fugitive John McAfee in Guatemala posted a photo of him online. The camera had embedded GPS coordinates automatically; the journalist had not thought to check. Researchers extracted them within hours, pinpointed the building, and authorities used the location to track him down. One photo. Zero hacking. Just metadata.
A quieter case shows how careful you have to be even when you try to protect people. In 2006, Wired reporter Quinn Norton photographed an anonymous source and cropped his face out — but knew the EXIF still held the GPS of his living room and an uncropped thumbnail. Her fix: she screenshotted the photo and sent that instead. Screenshots carry no camera EXIF, so the trail went cold.
For ordinary people, the risks are more mundane but just as real. A marketplace listing photo can carry your home's coordinates. A photo from your child's school carries a timestamp telling strangers when they are there. Enough geotagged photos strung together can map your weekly routine. And your device's make and model in a public photo tells an attacker exactly which "urgent security update" phishing message you would trust.
Which apps strip it — and which do not
Here is where most people get tripped up. Social media does not "remove all that stuff" the way you might assume — whether metadata survives depends on the platform, the feature, and the sending mode.
Big social feeds mostly strip it. Facebook, Instagram, X, TikTok, and LinkedIn re-encode photos for public posts, which wipes the EXIF. (They often keep the data internally — it is just not handed to other users.)
Messaging and sharing are where it leaks. Current testing (mid-2026): iMessage sends full GPS with photos picked from your album; WhatsApp document mode preserves 100% of metadata (a common trap — people use it to "preserve quality" and keep the GPS as a bonus); Telegram's send as file is byte-identical; and email, cloud links (Drive, Dropbox), and AirDrop all transmit the original file untouched. Forums, marketplaces, and small sites are inconsistent — many strip, many do not.
The one rule that makes all of this irrelevant: strip the metadata yourself before the file leaves your device. Then it does not matter what the platform does.
How to strip EXIF without uploading your photo anywhere
This is the part that surprises people. Removing EXIF does not require sending your photo to a server, an app company, or anyone. The pixel data and the metadata live in separate parts of the JPEG file — the EXIF block sits in a segment near the start, while the actual image comes after it. A tool running entirely in your browser can read your file into memory, cut that segment out, and hand you back a clean copy — the file never crosses the network.
That is exactly how Toolenix's EXIF Stripper works — everything happens locally on your device:
1. Open the tool in your browser. No account, no install, no upload. 2. Drop your photo onto the page. The file loads into your browser's memory — not a server. 3. Strip the metadata. The tool removes the entire EXIF block: GPS, device info, timestamps, embedded thumbnail, all of it. 4. Download the cleaned copy. Same resolution, colors, and quality — typically a few kilobytes lighter. 5. Verify if you like. Open the cleaned file in any free EXIF viewer and confirm the fields are gone.
Nothing was uploaded, so there is nothing on a server to leak or leave in a log file. Open your browser's developer tools and watch the network tab while you use it: silence.
A worked example: one phone photo, before and after
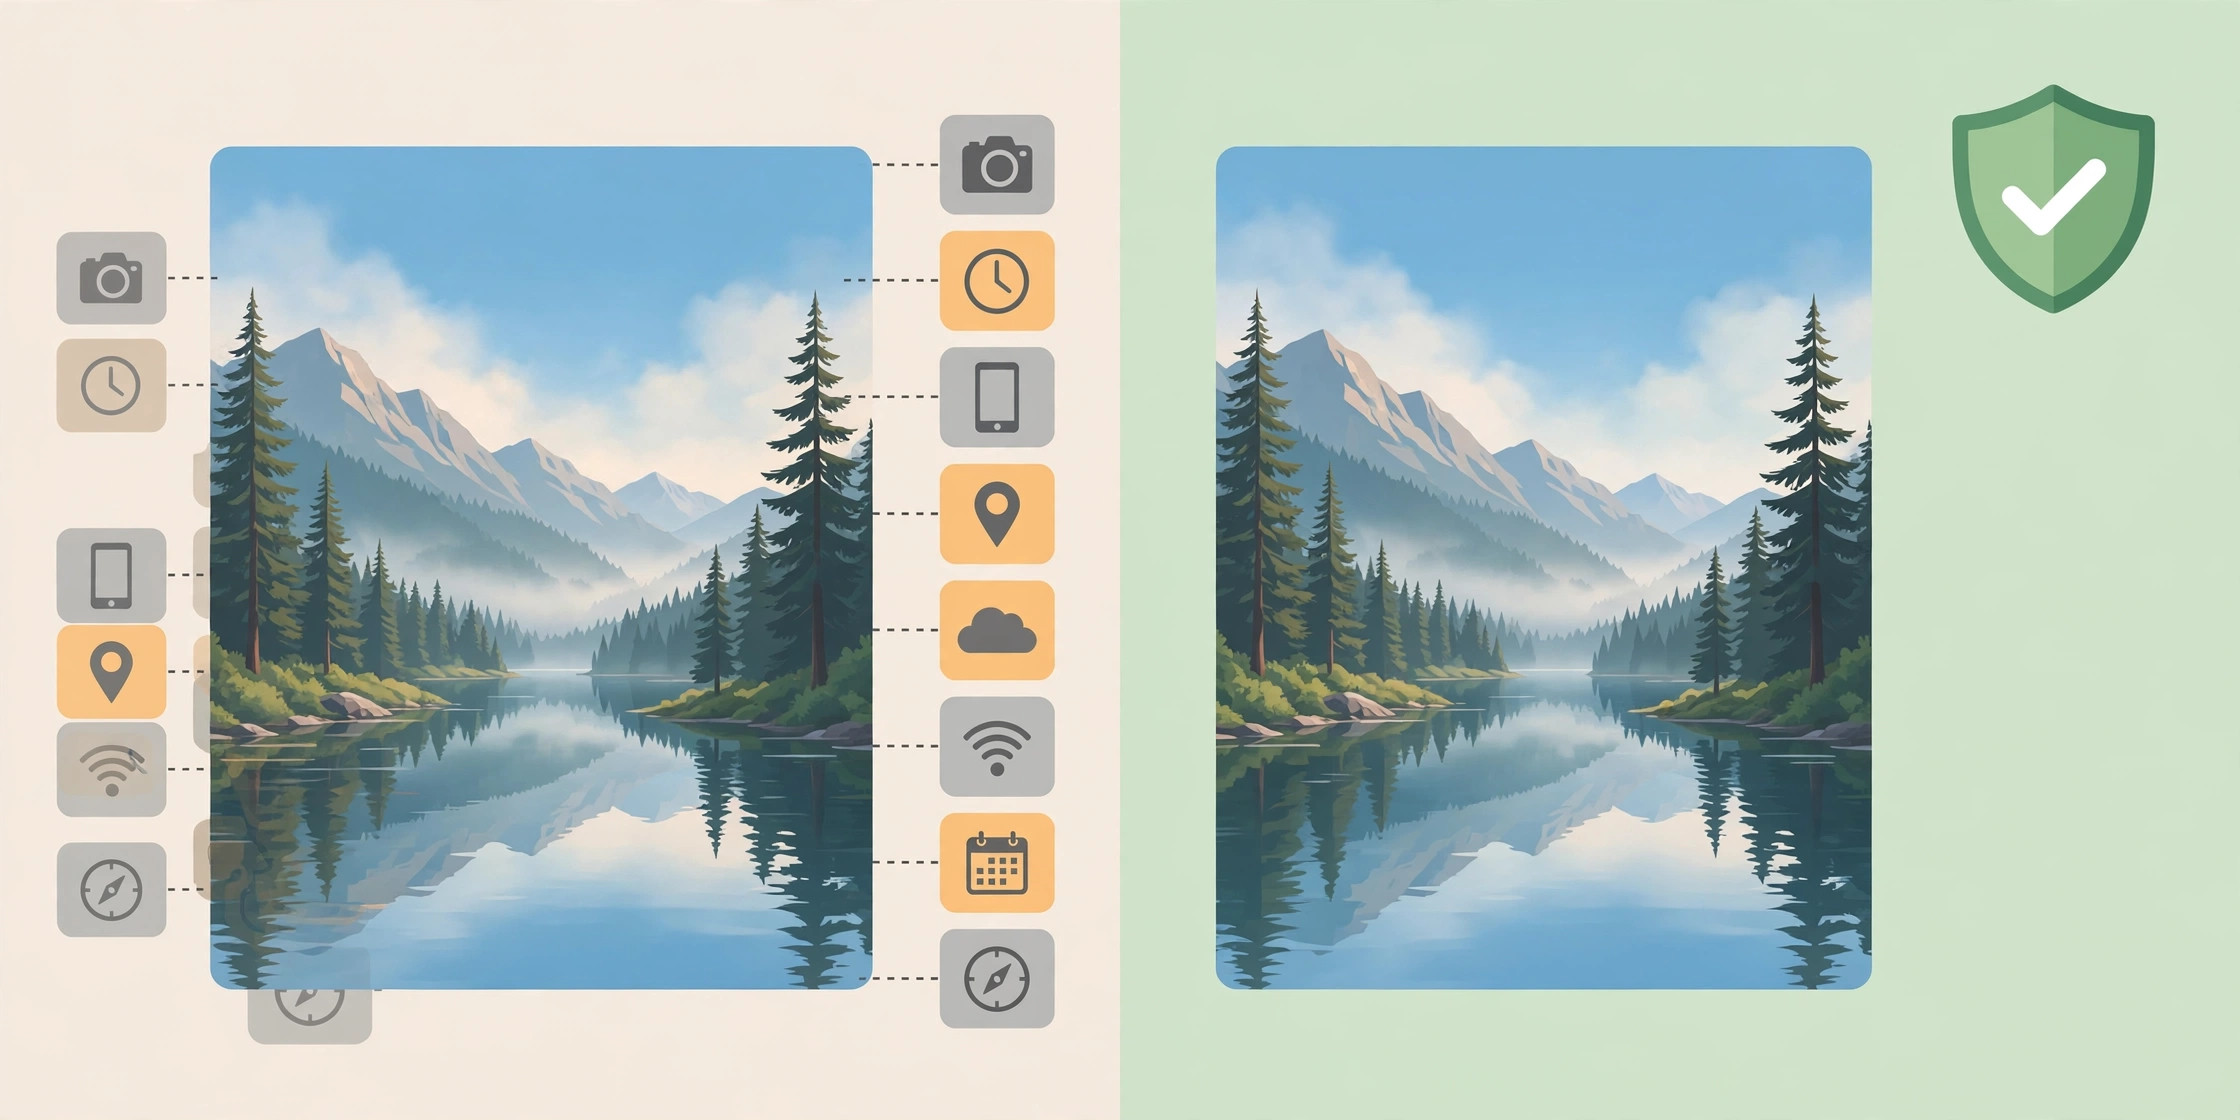
Let us make this concrete: a sunset from a rooftop, 4032 × 3024 pixels, 3.4 MB, location services on. Its EXIF block — about 28 KB — might contain:
- GPS: 40°42'46.1"N, 74°00'21.6"W — accurate to roughly a 4-meter radius, enough to identify a specific rooftop, and with it a specific building
- Altitude: 19 m above sea level
- Make / model: Apple / iPhone 14
- Serial number: a unique ID for this exact phone — every photo it ever posts can be tied to the same device, even across anonymous accounts
- Timestamp: 2026:10:06 18:32:14, to the second
- Settings: ISO 640, f/1.6, 1/60 s, 26 mm focal length
- Embedded thumbnail: a 160 × 120 version of the full, uncropped photo
- Artist field: sometimes auto-filled with the owner's name
Run it through EXIF Stripper and the output is 4032 × 3024 pixels, 3.37 MB — 28 KB lighter. Open it in an EXIF viewer and every item above reads empty, while the sunset is pixel-for-pixel identical.
That is the test you should run on any EXIF tool: strip a photo, then check the result in an independent viewer. If fields remain, the tool is not doing its job.
Mistakes to avoid
Only removing the GPS. This is not just a location problem — it is a metadata problem. The timestamp plus serial number can still identify you and reconstruct your schedule. Strip the whole block, not just the coordinates.
Trusting "remove properties" blindly on Windows. Windows Explorer clears some fields via right-click → Properties → Details, but misses others — including the embedded thumbnail. Verify with an EXIF viewer, or use a dedicated tool.
Cropping instead of stripping. A cropped photo can still carry the original uncropped thumbnail in its EXIF — Quinn Norton's 2006 problem, and it still works today. Cropping changes the pixels, not the metadata.
Sending as a "document" for quality. On WhatsApp, document mode preserves image quality — and 100% of the metadata. Strip the photo first, then send it however you like.
Forgetting that edits re-add metadata. Exporting an edited photo from an app often re-adds metadata, including the software name and new timestamps. Strip the exported file, not just the original.
Try it free — no sign-up
Run the numbers yourself in seconds. Everything happens in your browser.
Open the EXIF StripperFrequently Asked Questions
Does removing EXIF data reduce photo quality?
No. EXIF lives in a separate metadata header at the start of the file, so stripping removes that header without touching the pixel data. Resolution, colors, and compression are unchanged — the file just gets a little smaller.
How can I check what EXIF my photo has before stripping it?
Free viewers exist as browser tools and desktop apps (ExifTool is the classic); Windows also shows some fields under right-click → Properties → Details. Check first, so you know what you were about to share.
Do I need to strip photos before posting to Facebook or Instagram?
Their public feeds re-encode photos and wipe EXIF, so the feed pipeline is mostly safe. But DMs are leakier, the platforms may keep the data internally, and you might share the same photo elsewhere later — stripping first covers every destination.
What about PNG, WebP, or HEIC files?
EXIF is most associated with JPEG, but PNG can carry textual metadata chunks and HEIC photos from iPhones carry EXIF too. A good stripper handles the metadata sections of each format — same principle: remove the blocks, keep the pixels.
Can EXIF data be faked or wrong?
Yes. Timestamps come from the device clock, which can be wrong or deliberately set, and GPS can be spoofed. Treat EXIF as revealing but not proof — it says what the file claims, which is exactly why removing it protects you regardless of accuracy.
Is stripping EXIF enough to post a photo anonymously?
It removes the hidden data, but the visible content can still identify you: faces, street signs, license plates, reflections, landmarks. Strip the metadata, then re-examine the image itself with fresh eyes.